OCTOBER 15-18, 2013
SAINTCON has become the most important and effective security conference event in the State of Utah. We are proud to continue to serve the information security community by organizing this conference for 2013.
SAINTCON has become the most important and effective security conference event in the State of Utah. We are proud to continue to serve the information security community by organizing this conference for 2013.
This cost covers the following:
Access to all 4 Days of the Conference.
Lunch provided on-site Tues-Thur.
All-You-Can-Drink beverages during the con.
All Conference Equipment (~$70/person).
Dinner on Thursday Night.
Parking that the venue.
and much more...
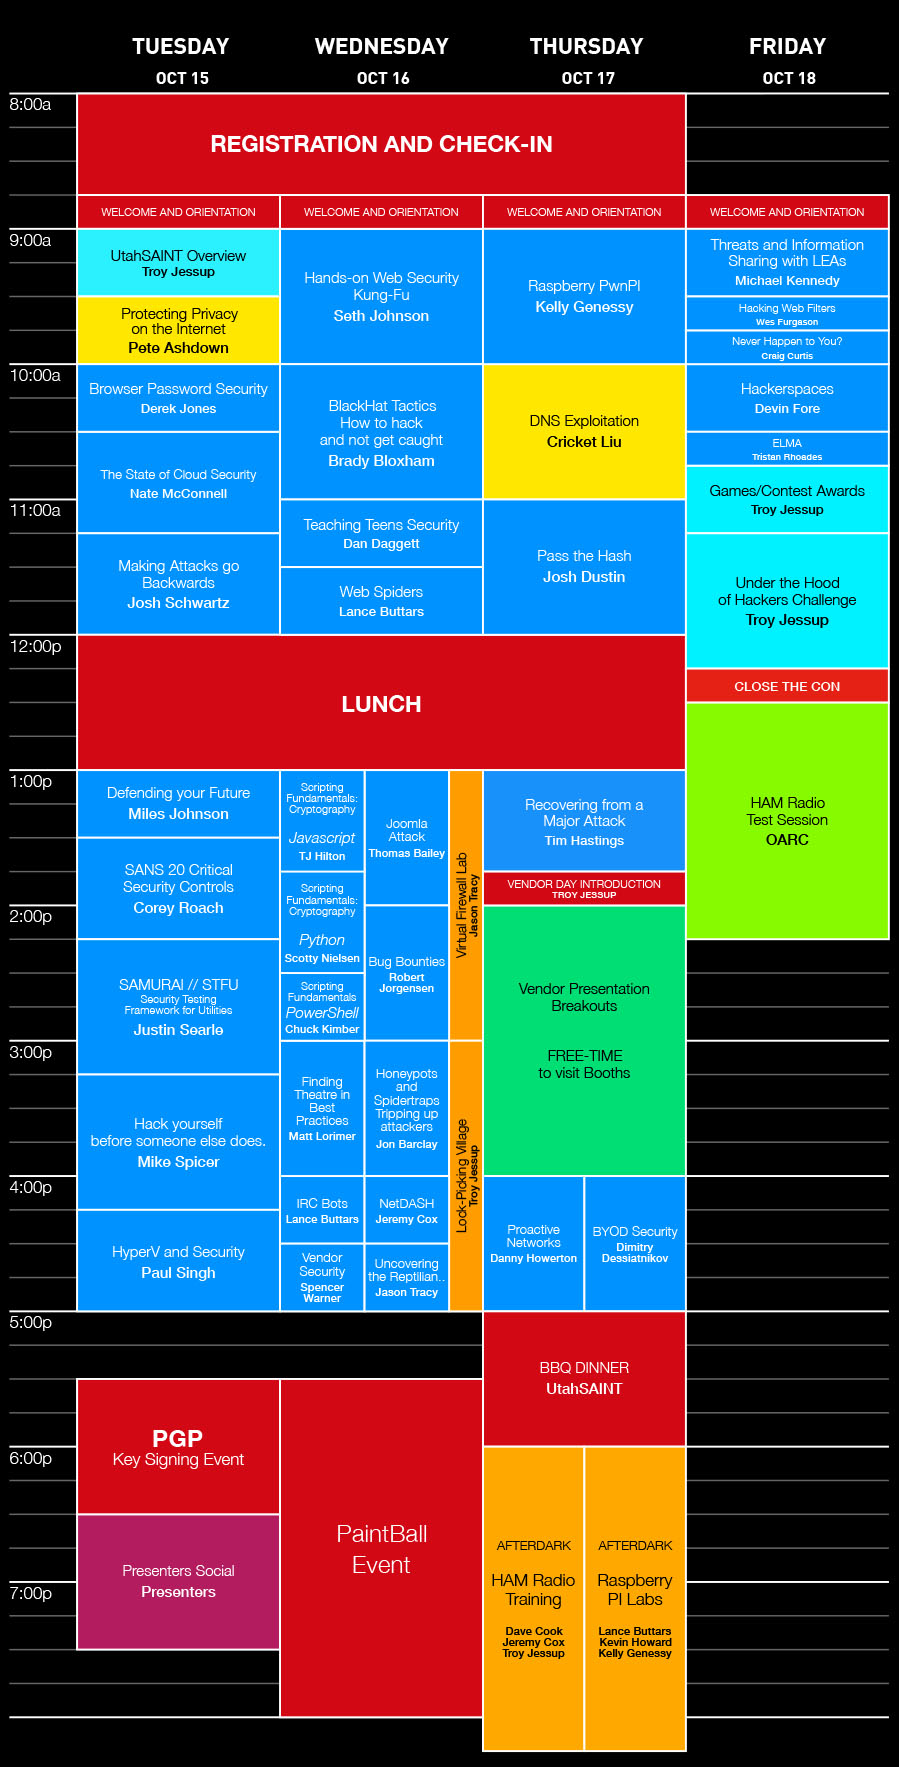
The following agenda is a final draft, but still subject to change
SAINTCON will be held at the Shepherd Student Union building at

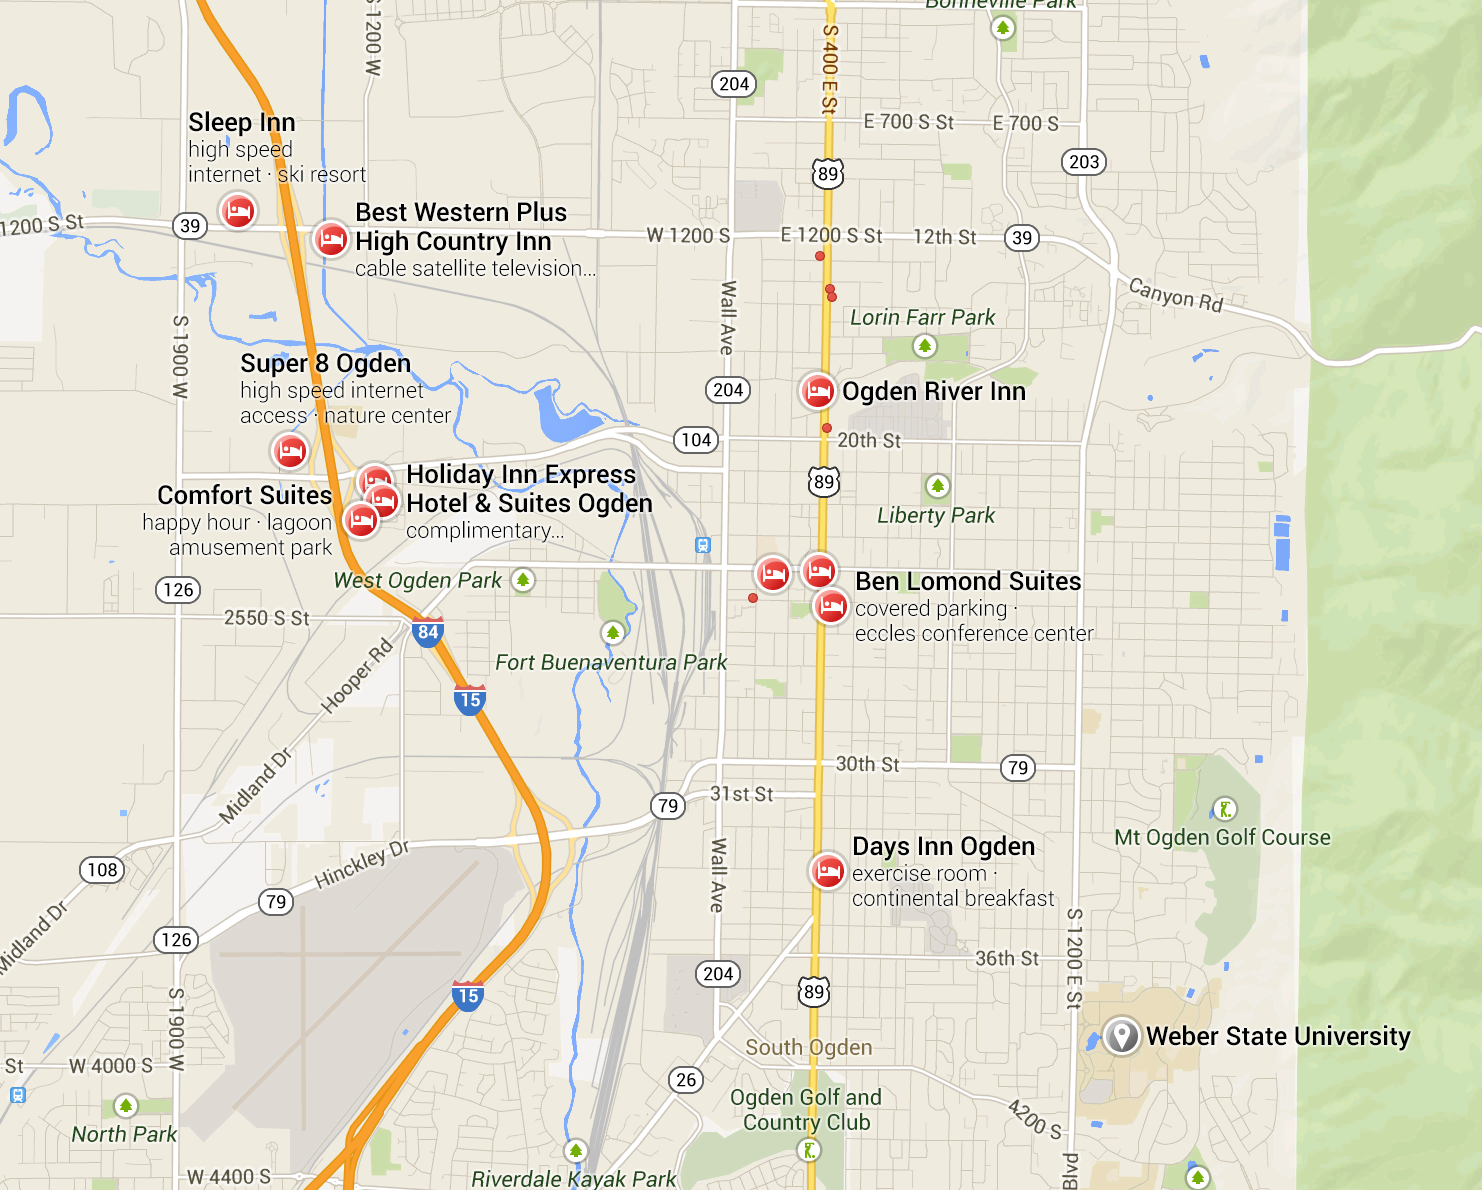
UtahSAINT will NOT be holding room blocks at any hotels this year.
Please make your housing arrangements EARLY or you may be sleeping on Luke's couch.
 The Summit 247 24th Street |
Hampton Inn and Suites 2401 Washington Blvd. |
Ben Lomond Suites 2510 Washington Blvd. |
 @SAINTCON #SAINTCON
Cricket Liu will be discussing the importance of understanding DNS exploits, and how the recent DNS exploits running rampant on the Internet are a threat to you. And if he gets a better abstract than this to us, we will put it up here.
For years we've had pen test distributions like BackTrack and SamuraiWTF to help us perform penetration testing in most IT environments, however these distributions have been generic in nature to enable their use in a wide variety of different environments. One environment where these distributions have failed to meet the needs of their users is on SCADA, Smart Grid, and other industrial control systems. We have just fixed this problem. Taking our experience running SamuraiWTF over the last four years, UtiliSec, a leading provider of security consulting services in the energy sector, has created an open source linux distribution specifically for Electric Utility security teams. SamuraiSTFU takes the best in bread security tools for traditional network and web penetration testing, adds specialized tools for embedded and RF testing, and mixes in a healthy dose of energy sector context, documentation, and sample files. Oh, and I shouldn't forget the inclusion of emulators for SCADA, Smart Meters, and other types of energy sector systems to provide leverage a full test lab. So whether work for an electric utility, or are interested in gaining sufficient experience to start doing security work in these environments, checkout the project at SamuraiSTFU.org
This presentation will focus on open source tools that lay traps that can actively block intruders, as well as alert defenders. It will use several of the tools in the Active Defense Harbinger Distribution (ADHD) in hands on labs.
Fun, Facts and Fiction of the Deep Net including a quick survey of the TOR network including .onion navigation, exit nodes, hidden service configuration, the literality of the "Primarch" system and more. Technical insight into the world beyond the surface web to include some cyber-crime underground and conspiracy theory.
This session will be a review of recent events regarding the NSA and the US government's spying program as revealed by Edward Snowden and provide a forum for discussion and debate.
This will be a general talk about security in the cloud. It will cover what as consumers of the cloud we can do to protect ourselves in either a public or private environment.
The FBI and Salt Lake InfraGard will provide a threat briefing applicable to Utah risks and show benefits of information sharing with the FBI on matters related to counterterrorism, cyber crime, fraud, and other major crimes.
The skills required to effectively defend are very different from the skills learned by attack.
Today's networks are purely reactive technologies in regards to security threats. Network and security admins are basically waiting for something to happen. I am going to talk about some easy, low cost ways that you can not only get more insight into your network but detect malicious activity before compromises happen.
We will review industry security guidelines and practices and sort useful security practices from the security theater.
Expose dangerous threats in your system or network before someone else does. This presentation discusses the mindset, tools and techniques the adversary has in their arsenal. Tools demonstrated are Nmap, TCPDump, Wireshark, NetCat, Dig and more. Demonstration will be Windows/Mac/*Nix friendly. By using the tools and techniques in this presentation you will be able to protect yourself from threats in a new way and stay one step ahead of the enemy.
Overview of fraud case and why having a plan is important. Will speak about issues and disconnects between departments.
This presentation covers a real world web server hack. Details include a timeline of reported incidents and our responses. Postmortem analysis establishes the timing and nature of the attack, as well as potential exposure. The perspectives of both the attacker and defender will be discussed.
I've always considered it best to not have browsers store passwords directly, but why? How easy can it be for malware to pull these passwords off of infected computers? Since sources are a bit tough to find in one place, I've decided to present the results here, as well as show some simple code to extract passwords from each browser's password manager.
Threats, attacks, and hacks are becoming more targeted and advanced. Hackers are using more and more stealthy and covert techniques to not only hack into organizations, but also cover their tracks, transfer money, and maintain good operational security. This presentation will cover the latest tactics and techniques that sophisticated hackers are using to remain uncaught while conducting blackhat operations. Understanding how attackers gain access, expand presence, and exfiltrate sensitive data is the first step in defending against it.
This year SocialGeeks planned and executed a Capture the Flag event at a small Idaho high-school. The 13 hour event included 20 students and 13 mentors (teachers and industry professionals). Not knowing what to expect, the skill level was aimed over their teachers head. The day consisted of lectures and a lot of hacking. By the end of the day, the teens, mostly without programming/linux experience, were coding solutions on linux machines and solving challenges. We would like to share this inspirational story with you and ask for help in going forward targeting teens with project and game based learning.
Your organization is only as secure as the sum of its parts including vendors and business partners. Information and suggestions on how to make sure that the companies you work with are as conscious about security as you are.
NetDash is a network dashboard and intrusion detection system. The System captures all traffic passed over the network and stores that traffic in a PCAP file that can be downloaded and analyzed with other tools such as Wireshark. NetDash processes each PCAP file and stores relavent information about each packet captured in a MySQL database. Loaded NetDash plugins display statistical and intrusion detection information on the dashboard and provide email and system notification of identified events.
Several large organizations, including Facebook, Google, and Mozilla, have turned to crowd-sourcing to find security and privacy flaws. Bug bounty programs pay users between $500 and $60,000 for locating and reporting security defects. Rob Jorgensen discusses the history and current state of bug bounties, his discovery of a logic flaw in Facebook that resulted in users sharing more than they intended, and his experience reporting the bug and being awarded a bounty.
"ELMA is a easy-to-use appliance that leverages the power of opensource software to enable you to quickly search through enormous amounts of logs. ELMA also provides visualizations of event frequency and dashboards with real-time updates. Much of the work is done by Kibana, ElasticSearch, and Rsyslogd. ELMA can be considered in the same category as Splunk. https://code.google.com/p/enterprise-log-management-appliance/
Explosion of mobile application market coupled with acceptance of "bring your own device" (BYOD) to enterprise environments comes with it's unique security risks. While driven by rise in productivity, convenience and overall user satisfaction BYOD increases the attack surface that most businesses are not prepared for. We will discuss the OWASP top 10 mobile risks and why should your business care about them. Practical recommendations and examples of common attacks will be presented.
An overview of the UtahSAINT organization, its progress for the past year, and how you can get involved. We will discuss upcoming changes to the organization and give a general report of what we are doing as an organization.
We will be re-covering the lock-picking concepts we covered last year. This is generally for those new to the conference and who want to learn more about how locks work. If you came last year, you might be bored this year unless you forgot everything.
For those of you who come to SAINTCON to play Hackers Challenge, you will not want to miss this. During this presentation we will cover each and every Hackers Challenge puzzle and how to solve them. Everyone keeps asking about how to learn the skills to do this, and this year we will go in-depth and show you the tools and methods for solving these challenges.
In this presentation we will cover the cool things that you can do with a raspberry pi. We will specifically teach you how to use one for fun and pen-testing. and we JUST MIGHT GIVE ONE TO EVERYONE!
Websites are a part of our lives, and untold mountains of information and resources are currently available online. While this is a wonderful development for civilization, security professionals see the grim side effects: some studies suggest that more than 80% of websites have at least one *major* security vulnerability. Come participate in an interactive demonstration of common web security vulnerabilities, how to exploit them, and – most importantly – how to effectively secure them. Items on the agenda include: Injection, Authentication, Cross-Site Scripting, Object References, Security Configuration, Data Exposure, Access Control, Cross-Site Request Forgeries, Known Vulnerabilities, and Redirects/Forwards.
In this AfterDark event, we will be teaching the things you need to know in order to test for your HAM Technician Class License. We highly recommend that you study before-hand. We will provide recommended reading materials prior to the conference.
On Friday Afternoon, you will be given the opportunity to take the HAM Radio Exam. Anyone is welcome to take the test. Cost information will be posted as soon as we get it.
This session will offset the HAM Radio Class for those not interested in that, you can spend extra time playing around with your Raspberry Pi.
In this presentation we will discuss the use of the SANS 20 Critical Security Controls as a baseline security methodology for your organization. We will cover its purpose, and how to begin to adapt this methodology into your environment.
Hackerspaces are a great way to learn new things and share your existing knowledge with others. Join us to learn how you can help out.
"Pass-the-hash. The dreaded technique used to go from having access on a single machine to owning every machine in your environment. This presentation will show you multiple tools and techniques used by pentesters and our adversaries. By the end, beginners and experts alike will have a solid understanding of everything needed to pass-the-hash."
One of the latest products produced by Hak5, the Wifi Pineapple is an amazing tool that is relatively easy to deploy and can have devastating consequences within your organization. This device allows you to perform Man-In-The-Middle attacks to wireless devices of all kinds. Nearly all cell phones, laptops and tablets are vulnerable to the attack.
IRC is a great way to communicate with people. It is also a great way to communicate with computer systems. In this presentation you will be shown the basics of creating your own IRC bot using python and be provided a primer of the basics of IRC boting for error reporting and notification along with command and control.
In this talk we will cover how attacker tactics can leave behind obvious evidence, how their tools and can be identified and analyzed quickly, and how the human side of every attacker can lead to some great lulz. Attendees should leave armed with a variety of examples from the trenches of incident response and malware analysis that will give them an edge against the less advanced of advanced attackers. Key takeaways will include tips and tricks for identifying and reverse engineering malware and utilities used in targeted attacks as well as the forensic evidence they leave behind.
A Better description is coming soon, as soon as Chuck gets it to us..
The process and technology of hacking Web Filters
 The Hackers Challenge game is a competitive game that provides an opportunity for you to test your technical and security skills. This game promises to provide a great challenge to the attendees this year.
We are keeping many of the new aspects of the game secret this year, however we will be expanding the game board slightly this year. We will be making many challenges easier, and expanding the board to include more challenging puzzles as well.
The following challenge is provided to get the game going. There is nothing too complicated about this challenge, and if you complete it, you will have a significant advantage at a critical point in the game. You will need the following to start:
aHR0cDovL3d3dy5zYWludGNvbi5vcmcvaGMxLwo=
First to solve was metacortex
Your challenge begins here: www.saintcon.org/hc2/.
This challenge will require that you connect to port 20001 on www.saintcon.org
NOTE: There is a 20 second delay after each connection before the port opens again. Be patient, and you do not need to pound on it.
WEB BROWSER NOT REQUIRED
Hint #1: 1, 2, R, B.
Hint #2: One Fish, Two Fish, Red Fish, Blue Fish. (Added Sep 21, 9:50a)
Hint #3: Your next hint is here: SAINTCOT (Added Sep 21, 11:30a)
Hint #4: Added to the bottom of the previous LINKED PAGE
More Hints will Follow from time to time until it is solved
 HAM RADIO TRAINING
There has always been a lot of interest in HAM radio by many of the members of UtahSAINT. This year we will be teaching the HAM Radio Technician Class material. The intent is that an attendee of the conference should be able to take this training, and review the study materials and likely be able to pass the test.
The Ogden Amateur Radio Club will be administering the test on Friday Afternoon immediately following the conference. It is scheduled to start at Noon, and will last a couple of hours.
We Strongly recommend that you study BEFORE coming to the conference. Having a basic understanding of radio technologies will be very helpful and will increase your ability to leverage the training you will receive at SAINTCON. To that end, we would highly recommend that you reference the folling sites and study the materials
Helps you understand what you need to know.
These are great for craming just before the test.
I recommend you take this over and over.
For you to Register your FRN (Recommended)
It is an event to get together and meet other PGP users and sign each others keys. This helps to extend the "web of trust" to a great degree. Also, it sometimes serves as a forum to discuss strong cryptography and related issues.
1. Physical attendance.
2. Positive government-issued picture ID.
3. Second proof of identity recommended. Picture not required.
4. Your key ID, key type, HEX fingerprint, and key size printed out.
This can be done by typing the following from your terminal:
$ gpg -K --fingerprint [your email]
5. A pen/pencil or something to write with.
I will need the following things from you in order to participate in the Key Signing Event at SAINTCON.
1. An Email with the subject "SAINTCON - My Public Key" (omit the quotes)
2. Attach your PUBLIC key to that email (.ASC) file or include it in the message body. You may attach more than one key if you have multiple keys
3. Please also ask any questions you have about the Key Signing Event
4. Send the email described above to: aaron[dot]toponce[at]gmail[dot]com
I will filter my email using the subject line above (so make sure you use it). I will determine who will be attending the event from the responses I get, and will print out fingerprints necessary for the event itself.
The fingerprint that you printed off, and brought with you to the event will be physically verified against the print off that I will bring to the event. After all fingerprints have been verified, we will take time to physically identify you and verify ownership of individual keys. Don't worry if this doesn't make sense right now, we will explain in painful detail at the event.
You will use your computer with the sheet we provide you at the event and sign everyone's key(s). An Event Keyring will be emailed to you to use for key signing.
I will be accepting emails with PGP PUBLIC Keys until October 14th. If you plan on being at the event, please submit your keys as soon as possible to ensure we have them ready. Individuals that have not sent me their key before the deadline will not be able to participate in the signing event. You may meet up with event attendees after the event is over and ask if they are willing to sign your key(s).
 As successful as this event was last year in pouring rain, we figure that an indoor event will be even better! This event is a lot of fun, and we encourage everyone to come out and play, even if you have never played before.
There will be a cost to participate in this event.
depending on how many people join us.
Food will be available for purchase at the venue if you get hungry.
Hackers Challenge Game
Will be coming back this year with all-new puzzles and more fun for both beginners and the advanced geeks.
PaintBall Tournament
Details are still being worked out, but we will be having a PaintBall event.
HAM Radio Training/Exam
For those who want to add HAM Radio to the geeky things you do, this activity will provide you with an opportunity to study for and take the HAM Radio License exam.
Presenters Party
Those presenting will be invited. More details to come.
AfterDark Labs
Geeks doing fun things in the night.. What more needs to be said.
PGP Key Signing Party
Every security con needs a key signing party. Come verify people you probably have never met IRL.